Get cyber-ready.
Get audit-ready.
See where you stand against your regulator's cyber, technology and operational expectations — and the evidence you'll need to close the gaps.
Built for Canada, the US, the EU and the Caribbean. Live today: OSFI B-10 · OSFI B-13 · PIPEDA · Quebec Law 25. In development: US, EU, Caribbean. Not legal advice or certification.
Cybersecurity requirements aren't just an IT problem.
Regulators expect you to govern cyber risk, control access, manage vulnerabilities, respond to incidents and demonstrate you can recover. RegLens shows you where you're ready — and where you're not.
- 1GovernanceNamed accountability and an approved policy
- 2Identity and accessLeast privilege, with MFA on privileged access
- 3Vulnerability managementContinuous monitoring and security testing
- 4Incident responseA plan that covers critical systems, and is tested
- 5Resilience and recoveryBackups shown to restore, recovery tested
Know what your regulator expects.
Each question shows the regulator's own text it rests on. See the expectation, assess your control, find the gap, and know what evidence to prepare. We never ask for your documents.
Live today
- OSFI B-13 Canada
In development
- CSA NI 31-103 Canada
- NYDFS Part 500 US
- DORA EU
- CIMA cybersecurity guidance Caribbean
- 1Expectation
- 2Assessment
- 3Gap
- 4Evidence
- 5Remediation
One assessment. Five audiences.
Answer once. Hand each reviewer the document they ask for, from the same answers.
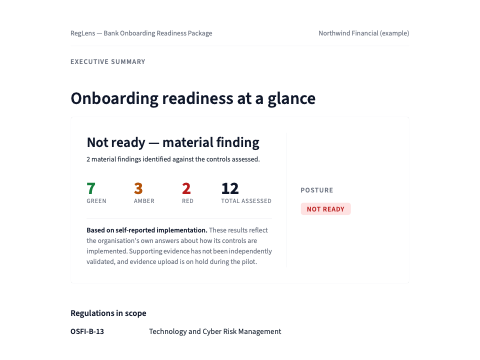
Bank vendor-risk teams
Bank Onboarding Package
Your answers arranged the way a bank's due-diligence review asks for them.
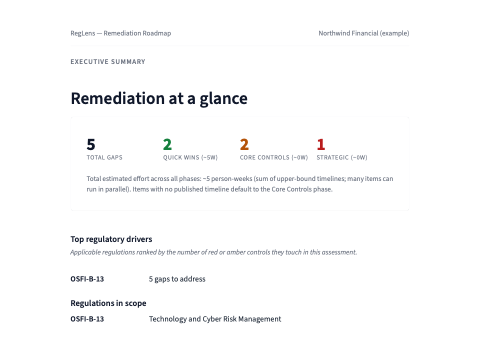
Your team
Remediation Roadmap
Every gap as an action, with owner, effort and timeline.
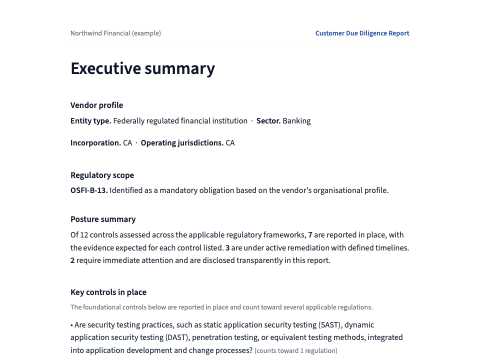
Customer procurement
Customer Due Diligence Report
An external-safe version that leaves out sensitive architecture.
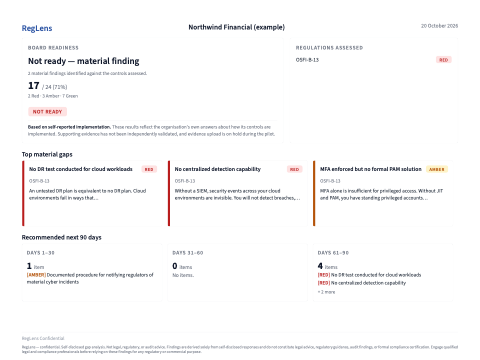
Board and executives
Board One-Pager
Where you stand, on one page.
Compliance and audit
Full PDF Report
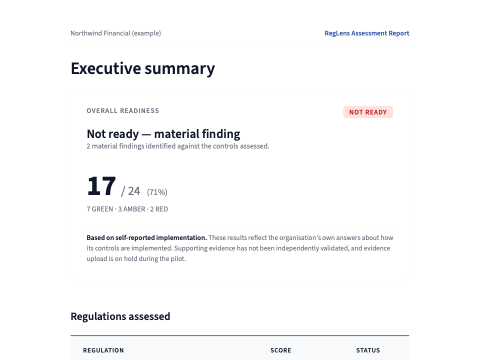
Every control, its status, the citation it rests on and the evidence to prepare.
See a real readiness package.
Generated by RegLens from a representative profile — the PDF a customer hands to a bank, an examiner or a board.

Featured sample
Awesome Inc.
Canadian federally regulated financial institution — OSFI B-10 third-party risk, OSFI B-13 technology and cyber risk, PIPEDA and Quebec Law 25.
Where RegLens works.
Built for Canada, the US, the EU and the Caribbean. A regulation goes live once its content has been read against the regulator's own text. This list is generated from our catalogue.
Canada
Live- OSFI B-10 — third-party risk
- OSFI B-13 — technology and cyber
- PIPEDA — federal privacy
- Quebec Law 25 — private-sector privacy
In development: CSA NI 31-103 — registrant cybersecurity
United States
In developmentIn development: FFIEC IT Examination Handbook · FINRA Rule 4370 — business continuity · GLBA Safeguards Rule — customer information security · Interagency guidance — third-party relationships · NCUA cybersecurity expectations · NYDFS Part 500 — cybersecurity · SEC cybersecurity and privacy rules
European Union
In developmentIn development: DORA — digital operational resilience · GDPR — data protection
Caribbean
In developmentIn development: Bermuda PIPA — privacy · BMA Operational Cyber Risk Management Code · Caribbean national cyber and financial codes · Cayman Data Protection Act · CIMA Statement of Guidance — cybersecurity · ECCB cyber expectations
Built on transparent methodology.
Every finding rests on a citation you can read. We publish how we decide what applies, what evidence we expect, and where our outputs stop: no legal advice, no audit certification, no regulatory approval.
- controls assessed
- 53
- controls assessed
- against the regulations live today
- regulations live
- 4
- regulations live
- assessed end to end today
- evidence expectations
- 228
- evidence expectations
- so you know what to prepare